Fractured Records, Hidden Abuses: The Reporting Failures That Protect US-Backed Security Forces
In the spring of 2021, human rights monitors documented a series of extrajudicial killings carried out by a Central American police unit with a well-established record of brutality. What made the episode particularly striking was not the violence itself — that, tragically, had become familiar — but the bureaucratic silence that followed. The unit had received both equipment and training through US security assistance programs. Yet no single federal database captured that connection in a way that would have triggered the legal vetting requirements designed to prevent precisely this outcome.
The gap was not accidental. It was structural.
Across the sprawling architecture of American security assistance — spanning the State Department's Foreign Military Financing program, the Defense Department's Section 333 authority, the Drug Enforcement Administration's international operations, and a constellation of smaller funding streams — data collection remains fragmented, inconsistently formatted, and rarely cross-referenced. The result is a reporting environment in which patterns of abuse can persist for years without generating the kind of consolidated evidentiary record that accountability demands.
A System Built for Opacity
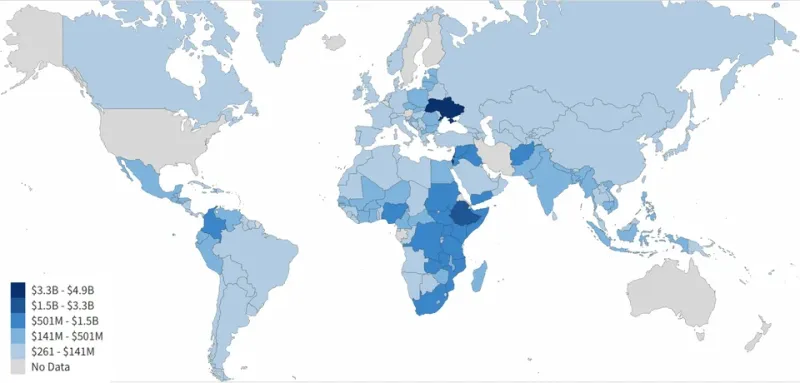
The United States funds, trains, or equips security forces in more than 150 countries. The legal frameworks governing this assistance — most notably the Leahy Law, which prohibits aid to units credibly implicated in gross human rights violations — require vetting processes that depend entirely on the quality and completeness of available data. When that data is fragmented, vetting fails. When vetting fails, abusers receive continued support.
The problem begins with how agencies define and record the units they assist. The State Department tracks recipients using one classification system; the Pentagon uses another. Regional combatant commands maintain their own operational logs, which are frequently exempt from routine disclosure. Intelligence community assessments that might flag problematic units are classified at levels that prevent their integration into civilian vetting databases. The outcome is not a single coherent picture of US security partnerships but a mosaic of incompatible datasets, each reflecting a portion of the whole and none sufficient on its own.
Researchers at several nongovernmental organizations who have spent years attempting to reconstruct US assistance flows describe the experience in remarkably similar terms: each data source they access reveals something the others obscure, and the act of reconciling them is itself a form of investigative labor that most oversight mechanisms are not designed to perform.
What the Metadata Reveals — and What It Hides
The evidentiary problem is not simply one of missing records. It is, more precisely, a problem of missing metadata — the contextual information that transforms raw data into actionable intelligence. A training record that identifies a recipient unit by name but omits its chain of command, its operational theater, or the specific personnel who participated provides almost no basis for cross-referencing against human rights incident reports. A funding disbursement logged under a program code without corresponding unit identifiers cannot be matched to field documentation of abuses.
This is not a hypothetical concern. Investigative journalists and human rights researchers have repeatedly demonstrated that units later implicated in massacres, forced disappearances, and torture maintained active relationships with US assistance programs — relationships that official records either failed to document adequately or actively obscured through classification. In several well-documented cases in Latin America and sub-Saharan Africa, the metadata necessary to establish these connections existed in scattered form across multiple agencies but was never aggregated in a way that would have triggered legal review.
The consequences extend beyond individual accountability failures. When patterns of abuse cannot be established from the available record, the political will to impose conditionality on security assistance evaporates. Congress cannot act on what it cannot see. Advocacy organizations cannot build cases without evidence. And the perpetrators — along with the governments that deploy them — learn precisely how much impunity the data architecture affords.
The Leahy Law's Structural Vulnerability
The Leahy vetting process, for all its importance as a legal instrument, is only as effective as the information environment in which it operates. Vetting units against credible allegations of abuse requires that those allegations be documented, accessible, and indexed in a format that vetting officers can actually use. In practice, the information environment is hostile to all three conditions.
Human rights incident reports generated by civil society organizations in recipient countries are rarely incorporated into official US government databases. Embassy reporting on security force conduct varies dramatically in depth and consistency depending on the priorities of individual ambassadors and political sections. The State Department's own human rights reports — the most comprehensive public source of country-level documentation — are produced annually and lack the granular unit-level specificity that vetting requires.
Meanwhile, the security assistance pipeline continues to move. Training rotations proceed on schedules that rarely pause to accommodate the slow accumulation of accountability documentation. Equipment transfers are processed through procurement channels that have no formal interface with human rights review systems. The temporal mismatch between the pace of assistance delivery and the pace of credible documentation is itself a structural feature of impunity.
Toward a Standardized Reporting Framework
Several advocacy organizations and a small number of former government officials have advanced proposals for reforming the data infrastructure underlying US security assistance accountability. The most substantive of these converge on a set of common principles.
First, unit-level identification must be standardized across all assistance programs. Every training event, equipment transfer, and funding disbursement should be recorded using a consistent identifier that enables cross-referencing across agencies and over time. The absence of this basic interoperability is the single most consequential gap in the current system.
Second, human rights incident data from civil society sources should be formally integrated into vetting databases. This requires not only technical infrastructure but institutional will — a commitment by the State Department and Defense Department to treat nongovernmental documentation as presumptively credible rather than presumptively suspect.
Third, the classification architecture governing security assistance records should be reformed to permit broader interagency sharing for vetting purposes, even where operational details remain restricted. The current system, in which the intelligence necessary to identify problematic units is siloed from the civilian processes responsible for approving assistance, is functionally incompatible with meaningful accountability.
Finally, Congress should mandate regular, publicly accessible reporting on the human rights performance of recipient units — not as a narrative summary but as structured data that researchers, journalists, and advocates can analyze independently. Transparency of this kind does not require disclosing sensitive intelligence; it requires only that the government commit to recording and sharing what it already knows.
The Stakes of Inaction
The argument for these reforms is not abstract. It is grounded in a documented history of American security assistance reaching units that went on to commit atrocities — and in the equally documented history of official records that failed to capture the connections that would have prevented it. The metadata gap is not a technical inconvenience. It is a mechanism through which accountability is systematically deferred and, in many cases, permanently foreclosed.
For the United States to credibly claim that its security partnerships advance human rights rather than undermine them, the evidentiary infrastructure must be capable of supporting that claim. At present, it is not. The fragmented, inconsistent, and often inaccessible data landscape that governs security assistance reporting ensures that the patterns most in need of scrutiny remain, by design or by negligence, beyond the reach of the oversight that democratic accountability requires.